As an org grows, "everyone can edit everything" stops being a feature and becomes a risk. PlanMagnet is governed from the start.
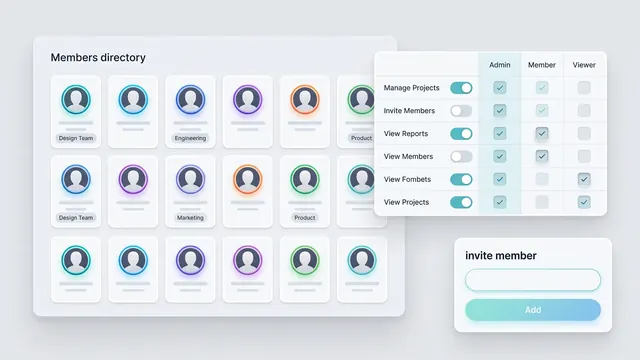
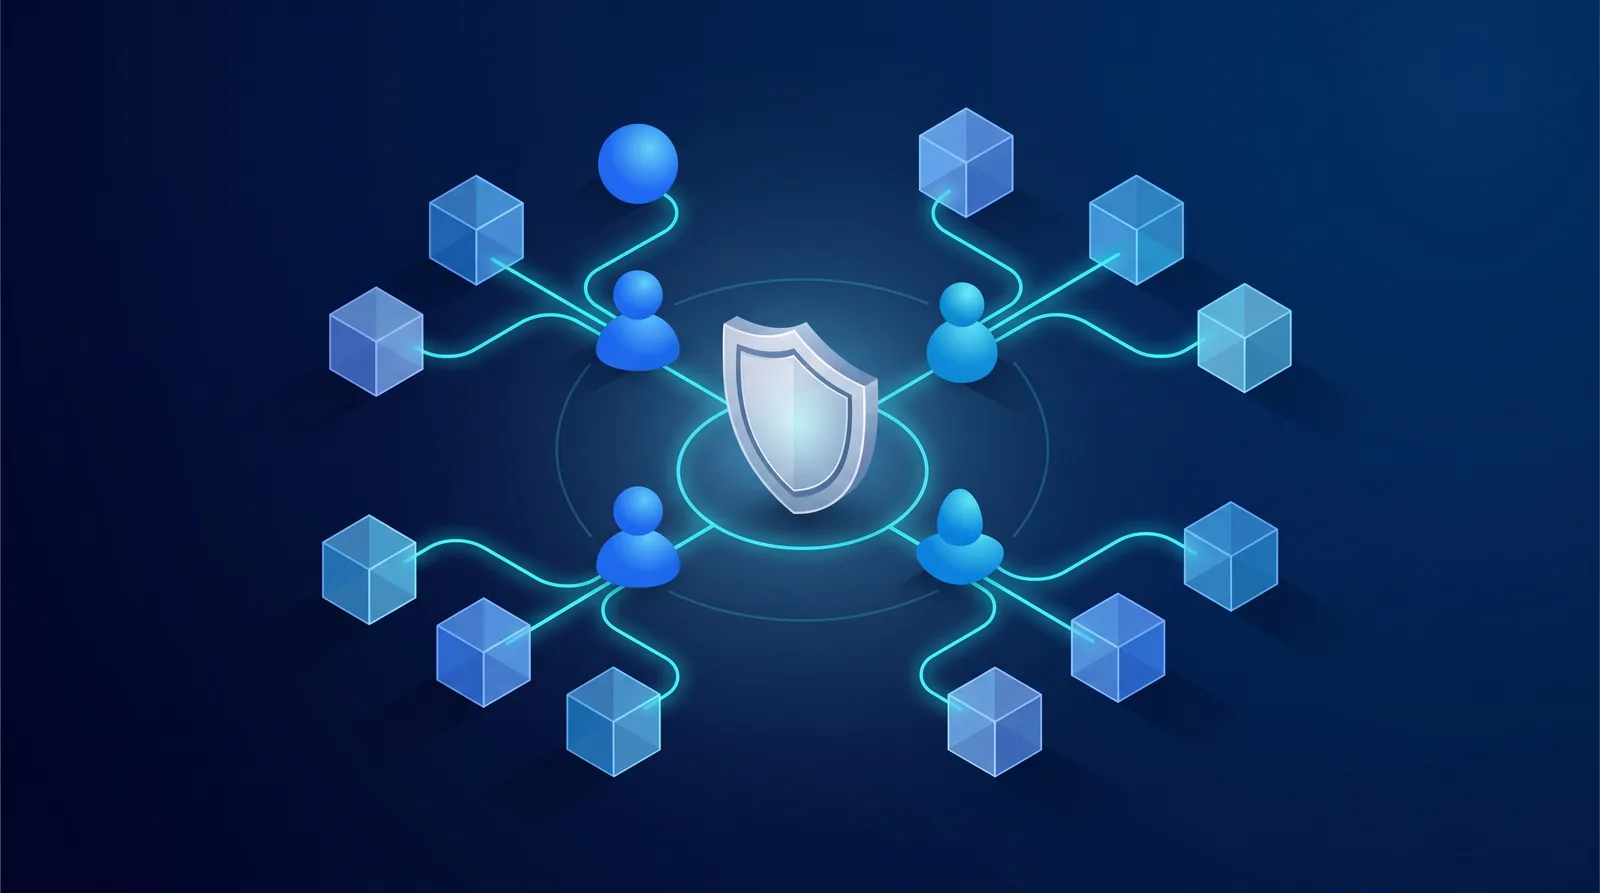
A workspace admin organises work into projects, assigns roles, and controls access with RBAC, so a contractor sees only their project and a guest stakeholder sees a read-only roadmap. Every change is attributable. Crucially, PlanMagnet does not reinvent any of this — identity and authorization are inherited from the Burdenoff platform.
That is how a workspace stays secure and auditable even as teams, projects, and external collaborators multiply.
Illustrative scenario — describing the identity and access model the platform is built on.
Illustrative planning guide
Run PlanMagnet as a governed multi-team workspace — isolate projects, assign roles, and control access with platform RBAC.
Open the Workspace page to set up the container that owns your projects, members, and roles.
You should see: Your workspace is ready, with governance built in from day one.
Ready to make this your story?